Proven Human Capital Management Solutions

Proven Human Capital Management Solutions

Proven Human Capital Management Solutions

We handle payroll, benefits, compliance and risk so you can focus on your business.

We handle payroll, benefits,

compliance and risk. You can focus on your business.

We handle payroll, benefits, compliance and risk so you can focus on your business.

Solutions Overview

HR Solutions That Work

Supporting clients with the services they need to succeed.

Partner for Growth

Why Outsource with C2

Businesses that outsource HR grow faster, achieve higher profitability, experience lower turnover, and foster happier employees. Stay focused on your business.

C2 will, too.

0
0

%

Clients Would Recommend

0
0

%

Increased
Profitability

0
0

%

Increase In Revenue

0
0

%

Lower Failure Rate

0
0

%

Improved
Retention

0
0

%

Costs

Savings

c2 connection

One Platform for All HR Needs

Your control center for HR, payroll, benefits, and compliance.

Home

Employment verification

Schedule

Payroll

Pay checks

Paid time off

PTO calculator

A task list on a sky background shows five items; two are "Completed," three are "Incomplete." "Forms are ready for E-sign" for "James Smith" with 4 days left.
Schedule
Carousel image
Carousel image
Carousel image
Carousel image
Carousel image
Carousel image

HR models

Choose the HR Model That
Fits Your Business

Choose the HR Model That Fits Your Business

Whether you need full-service co-employment or flexible admin support,
C2 offers the model that fits your growth stage and compliance needs.

Whether you need full-service co-employment or flexible admin support, C2 offers the model that fits your growth stage and compliance needs.

PEO - Professional Employer Organization

PEO Support — Make C2 Your Employer of Record

Let C2 become your Employer of Record so you can share liability, simplify HR, and access big-company benefits.

What’s Included:

Employer of Record: C2

Shared liability protection

Large-group health, dental, vision, and retirement benefits

Payroll & tax administration

Recruiting & HR support

ASO – Administrative Services Organization
PEO - Professional Employer Organization

PEO Support — Make C2 Your Employer of Record

Let C2 become your Employer of Record so you can share liability, simplify HR, and access big-company benefits.

What’s Included:

Employer of Record: C2

Shared liability protection

Large-group health, dental, vision, and retirement benefits

Payroll & tax administration

Recruiting & HR support

ASO – Administrative Services Organization
Proof & Trust

Trusted by Businesses Nationwide

“C2 helped us capture new contracts and scale our organization not only through its robust HR services, but especially because of its expertise in the government contracting space.”

James Smith, CEO

0
0
0

+

+

+

Clients

Clients

0
0
0

+

+

+

Years in business

Years in business

0
0
0

+

+

+

Happy users

Happy users

0
0
0

States serviced

States serviced

0
0
0

+

+

+

Countries serviced

Countries serviced

0
0
0

%

%

%

Federal contractor client base

Federal contractor client base

Proof & Trust

Trusted by Businesses Nationwide

“C2 helped us capture new contracts and scale our organization not only through its robust HR services, but especially because of its expertise in the government contracting space.”

James Smith - CEO

0

+

Clients

0

+

Years in business

0

+

Happy users

0

States serviced

0

+

Countries serviced

0

%

Federal contractor client base

Blog

Stay Ahead of HR Trends

North Korean IT Worker Schemes: What Employers and Government Contractors Should Know

On October 13, 2026, the U.S. Department of Justice announced coordinated enforcement actions targeting North Korean remote IT worker schemes. The actions included arrests, an indictment, searches of suspected “laptop farms” and the seizure of approximately 187 computer devices. DOJ said the schemes affected more than 70 U.S. companies. The cases underscore a risk for organizations that hire remote technology workers or rely on outside staffing and IT vendors: a person who appears to be a qualified U.S.-based applicant may be using a stolen or fabricated identity on behalf of North Korean networks.


The alleged objective is not simply to obtain a paycheck. Revenue generated through these placements can support the North Korean regime and its prohibited programs. Once hired, workers may also gain access to internal systems, source code, customer information, credentials or other sensitive business data. The FBI has warned that some schemes have involved theft of proprietary information and extortion.

How the schemes work

According to U.S. government advisories and recent cases, individuals may apply using stolen identities, fabricated credentials, alias email accounts and misleading online profiles. They may use VPNs, proxy infrastructure or remote-access arrangements to make it appear they are working from a U.S. location. In some cases, people in the United States help receive company laptops, establish internet connections, create accounts or otherwise facilitate the arrangement. Some facilitators may knowingly assist; others may be misled.


A company may therefore ship a device to a seemingly legitimate worker while the person actually operating it is elsewhere. The person who passes the interview may not be the person doing the work. In addition, a staffing supplier or subcontractor can create distance between the employer and the person ultimately accessing company systems. The FBI has specifically cautioned businesses to assess third-party hiring and remote IT arrangements, not only direct hires.

Why government contractors should pay attention

Small and mid-sized government contractors can be attractive targets because they often need specialized technical talent, work with subcontractors and support distributed teams. A fraudulent placement may create several overlapping risks: unauthorized access to government-contract information, exposure of controlled or proprietary data, credential theft, intellectual-property loss, sanctions concerns, disruption to contract performance and reputational damage. Whether a particular incident triggers a contractual or regulatory reporting duty depends on the contract, data involved and applicable requirements; organizations should involve their security, contracts and legal teams promptly rather than assume one reporting rule fits every situation.


The risk is not limited to classified work or large defense companies. Any organization that provides access to business networks, code repositories, cloud services or client environments should consider how it verifies the identity and location of remote workers and how it limits access after onboarding.

Practical steps to reduce risk

Strengthen identity verification at several points—not only when an offer is made.

  • Verify identity documents and compare the applicant’s name, photograph, contact information, employment history and education using independent sources.

  • Check for repeated resumes, email addresses, phone numbers, banking details or other information across apparently unrelated applicants.

  • Where feasible and appropriate, use live video verification and in-person steps for roles with elevated access.

  • A mismatch is a reason to pause and verify, not to make assumptions based on nationality, accent or other protected characteristics.

Control equipment and access.

  • Send company devices only to a verified address and require additional review if an applicant requests a last-minute shipping change or a third party to receive equipment.

  • Do not grant production, customer or sensitive-data access before required identity and background checks are complete.

  • Use least-privilege permissions, restrict local administrator rights and limit installation of remote-access tools.

  • Monitor for unusual logins, geographically inconsistent connections, unexpected remote desktop software, repeated account changes, or unusual transfers to personal cloud storage and code repositories.

Review vendors and subcontractors.

  • Ask staffing firms how they verify identity, confirm the actual worker assigned to a role and prevent undisclosed substitution or subcontracting.

  • Make sure contracts establish appropriate security expectations, audit rights and escalation procedures.

  • For higher-risk IT roles, consider periodic identity checks and confirm that the person performing the work is the person approved by the company.

  • Train recruiters, HR, hiring managers and IT/security staff together so warning signs are not treated as isolated administrative issues.

If you suspect a fraudulent placement

  • Escalate concerns immediately to information security, HR, legal and the contract/security lead.

  • Preserve relevant hiring records, messages, device information and access logs.

  • Avoid alerting a suspected actor in a way that could compromise an investigation.

  • Security staff should assess whether credentials need to be disabled, sessions revoked, devices isolated or data access reviewed, while preserving evidence and maintaining business continuity.


The FBI recommends reporting suspected North Korean IT worker activity to the local FBI field office and the Internet Crime Complaint Center (IC3). Contractors should also review any applicable contract clauses, incident-response plans and customer notification requirements with the appropriate internal teams. Report suspected activity based on the facts and applicable obligations, not on a single indicator alone.

Bottom line

Remote hiring controls are now part of both workforce risk management and cybersecurity. Contractors do not need to abandon remote work, but they should verify identity and work location, scrutinize third-party arrangements, limit access to what each worker needs, and monitor for suspicious activity throughout employment—not just at the application stage.

Useful links

  • U.S. Department of Justice: October 13, 2026 enforcement announcement

  • FBI: North Korean IT worker threats to U.S. businesses

  • FBI: North Korean IT workers conducting data extortion

Read more

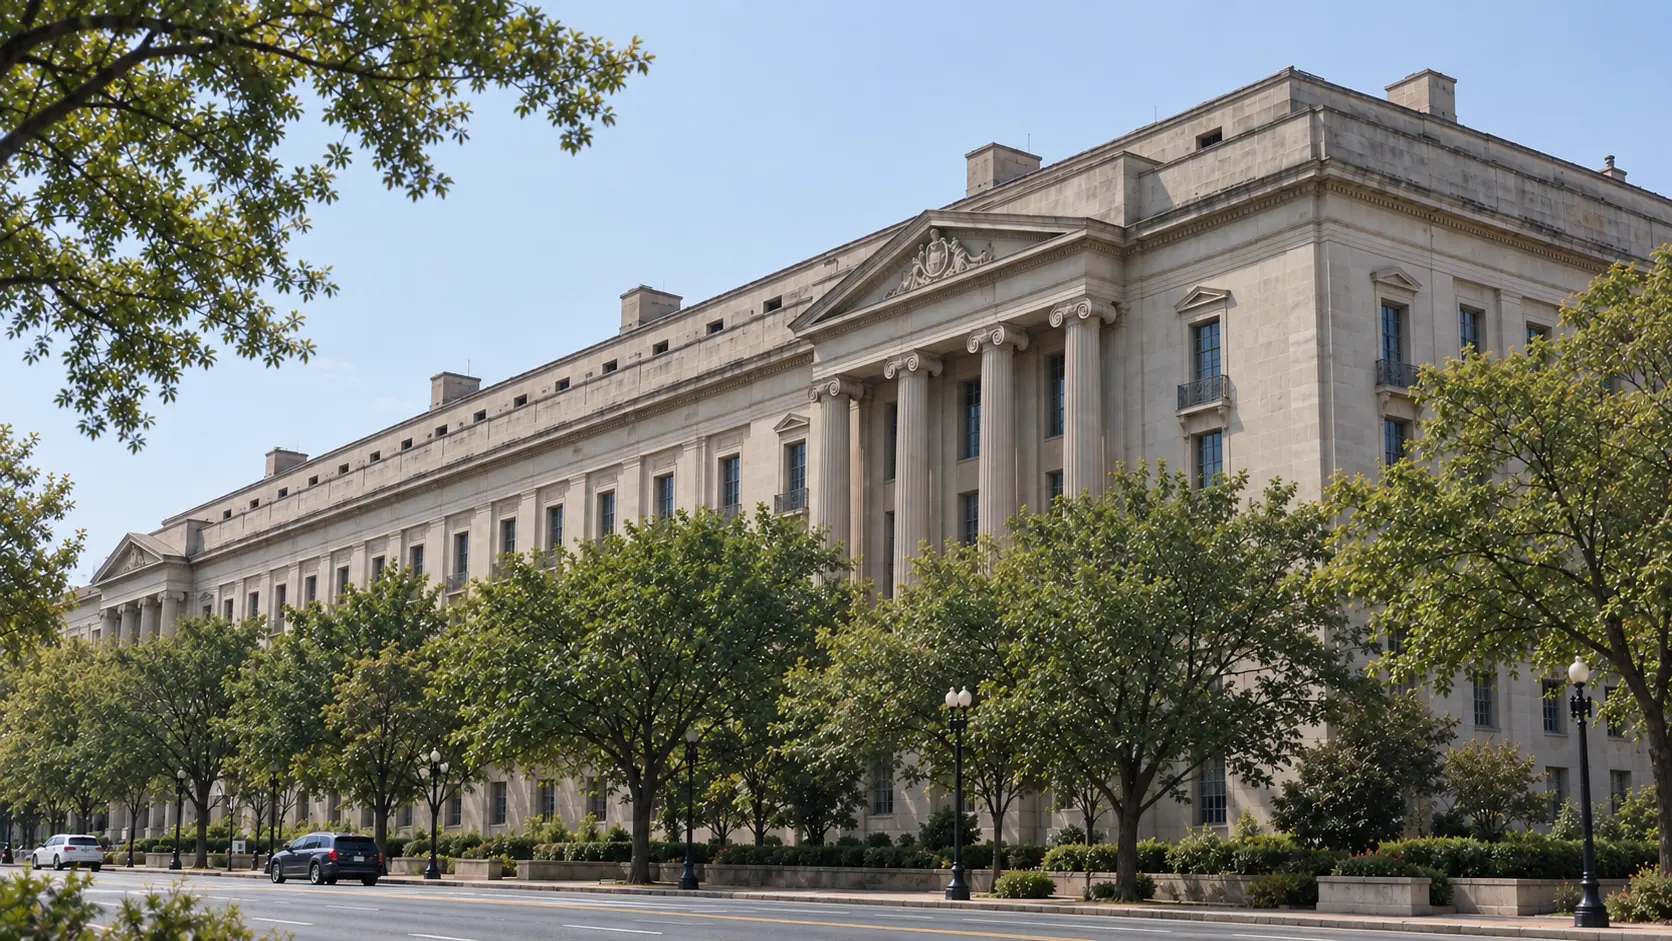
Exterior of a large neoclassical government building with columns, lined by mature trees and a street

DOJ Increases Focus on Federal Contract Fraud

The U.S. Department of Justice (DOJ) has announced new national fraud enforcement priorities that may be particularly relevant to federal government contractors. In a memorandum, DOJ identified government procurement fraud as a critical enforcement priority and outlined an increased focus on fraud involving government contracts and taxpayer-funded programs. 


The Department's new National Fraud Detection Center brings together prosecutors, law enforcement agencies, data analysts, and subject-matter experts and uses advanced data analytics to identify potential fraud and develop investigative leads. 


The DOJ identified several areas for increased enforcement attention, including defective pricing, bid rigging, self-dealing, bribery, product substitution, and billing fraud. DOJ also plans to use increased data analytics and coordination among federal enforcement agencies to identify and investigate potential fraud. 

Existing Contractor Requirements Remain Important 

The DOJ announcement does not create a new general compliance requirement for all government contractors. Many of the applicable ethics and disclosure obligations have been part of the Federal Acquisition Regulation (FAR) for years. 


For example, FAR 52.203-13, Contractor Code of Business Ethics and Conduct, applies to certain covered federal contracts and requires contractors to maintain a written code of business ethics and conduct and establish appropriate measures to prevent and detect criminal conduct.  Under the current FAR, the clause is generally included in contracts expected to exceed $7.5 million with a performance period of 120 days or more.  


Covered contractors also have requirements related to internal reporting, training, internal controls, and disclosure of certain credible evidence of misconduct. The increased DOJ enforcement focus provides a good reason for government contractors to review whether their existing compliance processes are current and functioning as intended. 

How Issues May Be Identified 

Government contractors should be aware that potential compliance issues may be identified through employee or former-employee reports, government audits, agency Inspectors General, contracting officials, whistleblower lawsuits, or increasingly through data analytics that identify unusual patterns in government contracting and payment data. 


The government's own description is that it is trying to connect information that previously existed in separate systems and use analytics to generate investigative leads.   


If the government identifies potential misconduct, the contractor may face an investigation, audit, civil or criminal enforcement action, repayment or settlement obligations, and, in serious cases, suspension or debarment from federal contracting. A typical progression can look like this: 


  1. Initial inquiry/investigation. DOJ, an agency Inspector General, or another government agency may request records, interview employees, or investigate the allegation. In False Claims Act matters, DOJ has authority to issue a Civil Investigative Demand (CID) seeking documents, written answers, and/or oral testimony.  


  1. Internal investigation and cooperation. If FAR 52.203-13 applies, the contractor has obligations concerning cooperation with government audits/investigations. The clause also expressly preserves the contractor's ability to conduct its own internal investigation and defend a proceeding.  


  1. Civil settlement or recovery. If the government concludes that the contractor improperly billed or made false claims, the matter can result in repayment, penalties, or a negotiated settlement. The dollar amounts can be substantially larger than the underlying improper payment.  


  1. Criminal prosecution. If the evidence supports criminal conduct, DOJ can pursue criminal charges against the company and/or individuals.  


  1. Contract consequences. Depending on the circumstances, the contractor can face contract remedies, including termination, withholding/recovery of payments, or other administrative action.  


  1. Suspension or debarment. This is potentially the most significant contractor consequence. FAR permits suspension when there is adequate evidence of certain misconduct, including fraud or criminal conduct relating to a government contract. Suspension is temporary and generally remains in effect while an investigation or legal proceeding is pending.  


Recent Enforcement Examples 

Recent DOJ enforcement actions demonstrate the types of issues that can create significant exposure for government contractors: 


Compliance
Area 


DOJ Enforcement 


HR/Compliance Takeaway 


Labor charging 


March 2026 – Hanford Mission Integration Solutions (HMIS): HMIS agreed to pay $3.45 million to resolve allegations that it overcharged the Department of Energy for labor hours. DOJ said management was aware of and failed to prevent inflated labor hours, including employees recording time for work they had not been assigned. The settlement included $1.725 million in restitution and followed whistleblower allegations from an employee. 


Accurate timekeeping, labor charging, work assignments, and manager oversight are important controls for contractors, particularly those performing cost-reimbursement work. 

This is one of the areas where DCAA-compliant payroll systems become critical, as they maintain the audit trail the government expects


Cybersecurity requirements 


September 2026 – Honeywell Aerospace: Honeywell agreed to pay $2.04 million to resolve allegations that it submitted claims for payment while failing to comply with NIST SP 800-171 cybersecurity requirements incorporated into a Department of Defense contract. The matter arose from a False Claims Act lawsuit filed by a former employee, who will receive approximately $375,823 from the settlement. 


Employees who handle government information should understand applicable cybersecurity requirements and know how to report concerns. Contractors should maintain appropriate channels for current and former employees to raise potential compliance concerns. 

Cybersecurity is one of six federal contracting changes every government contractor should know about in 2026, including CMMC readiness requirements.


Organizational conflicts of interest 


July 2026 – Sierra Nevada Company: Sierra Nevada agreed to pay $7.75 million to resolve False Claims Act allegations involving its employment of a government employee who continued participating in contracts involving the company. DOJ alleged that the arrangement created an organizational conflict of interest and that the company made false statements and certifications concerning the conflict. 


Hiring or employing current or former government personnel can create compliance considerations. Contractors should have a process for identifying and escalating potential conflicts before an individual participates in contract-related activities. 


Small-business and SDVOSB requirements 


June 2026 – Broadway Electric and Cornerstone Contracting: The companies and two executives agreed to pay $21.3 million to resolve allegations involving the improper use of federal contracts reserved for service-disabled veteran-owned and other eligible small businesses. DOJ alleged improper control over staffing, performance, and financial administration of purported qualifying businesses. 


Contractors participating in set-aside programs should periodically verify that ownership, control, staffing, performance, and other representations remain accurate. 


Contractor kickbacks 


July 2026 – Mark 1 Restoration Company: Mark 1 and its owner agreed to a $7.26 million resolution of civil claims involving alleged kickbacks paid to an Amtrak official to obtain favorable changes to a government contract. The owner and several executives had previously pleaded guilty to related criminal charges. 


Contractors should ensure employees and managers understand restrictions concerning gifts, gratuities, kickbacks, conflicts of interest, and interactions with government officials. 


These cases illustrate that government-contract enforcement can involve timekeeping and labor charging, cybersecurity, conflicts of interest, small-business eligibility, procurement practices, billing, and employee reporting. They also demonstrate that issues can be identified through employees, former employees, agency inspectors general, and other government enforcement resources. 

What Government Contractors Should Review 

Contractors should consider the following: 

  • Don’t just have policies on paper. Make sure employees know the rules, managers understand their responsibilities, time and billing records are accurate, and there is a functioning process for reporting and escalating concerns—including a confidential or anonymous reporting option. 

    A PEO built for government contracting can help maintain these controls across payroll, benefits, and compliance without building the entire infrastructure in-house.


  • Review applicable contracts. Determine whether FAR 52.203-13 or other agency-specific ethics and disclosure requirements apply to current contracts or subcontracts. 


  • Review the code of conduct. Confirm that the company's business ethics and conduct policy is current and accessible to employees. 


  • Confirm reporting procedures. Employees should know how to report suspected fraud, conflicts of interest, bribery, improper billing, or other potential misconduct. 


  • Review training requirements. Confirm that employees and other covered individuals receive required ethics and compliance training. 


  • Review internal controls. Pay particular attention to controls involving government billing, labor charging and timekeeping, pricing, procurement, subcontractors, cybersecurity, and contract deliverables. 


  • Reinforce non-retaliation expectations. Employees should be able to raise concerns through established reporting channels without fear of retaliation. 


  • Review escalation procedures. Managers should know where to direct concerns involving potential government-contract misconduct rather than attempting to resolve significant allegations independently. 


  • Review disclosure procedures. Make sure the company has a process for promptly involving the appropriate compliance and legal resources when potential misconduct may trigger a contractual or legal disclosure obligation. 


  • Document corrective action. Where concerns are substantiated, companies should document appropriate corrective and remedial measures consistent with their policies and contractual requirements. 


If you're a government contractor reviewing your compliance posture in light of these DOJ priorities, C2 Essentials works with federal contractors to maintain DCAA-compliant payroll, accurate labor distribution reporting, and the documentation standards that keep your contracts defensible. Talk to our team about what a compliance review looks like for a company your size

Government Resources 

  • U.S. Department of Justice – Fraud Section: https://www.justice.gov/fraud 


  • DOJ – Fraud Division Policies and Guidance: https://www.justice.gov/criminal/criminal-fraud/policy-materials 


  • Acquisition.gov – FAR 52.203-13, Contractor Code of Business Ethics and Conduct:  https://www.acquisition.gov/far/52.203-13 


  • Acquisition.gov – FAR Subpart 3.10, Contractor Code of Business Ethics and Conduct:  https://www.acquisition.gov/far/subpart-3.10 


  • Acquisition.gov – FAR 3.1003, Requirements for Government Contractors:  https://www.acquisition.gov/far/3.1003 

Read more

Futuristic quantum computing microchip on circuit board representing advanced technology

Quantum Computing: Why Government Contractors Should Be Paying Attention 

Quantum computing may sound like a technology reserved for scientists and large technology companies, but recent federal investments suggest it is becoming increasingly relevant to the government contracting community. 


The latest development: IBM has finalized a $1 billion award from the U.S. Department of Commerce to support research and development at a new U.S.-based quantum chip foundry. The facility, known as Anderon, is being developed to manufacture specialized quantum computing wafers and help expand the domestic quantum technology supply chain. 


The IBM announcement is part of a much larger federal effort. In May 2026, the U.S. Department of Commerce announced $2.013 billion in planned CHIPS and Science Act incentives for nine companies across the quantum computing and manufacturing ecosystem, including IBM, GlobalFoundries, D-Wave, Quantinuum, PsiQuantum and other emerging quantum technology companies. 

First, What Exactly Is Quantum Computing? 

In simple terms, a quantum computer is a fundamentally different type of computer. Today's computers process information using bits, which represent either a 0 or a 1. Quantum computers use qubits, which can take advantage of unusual properties of quantum physics to process certain types of problems in ways that conventional computers cannot.


That does not mean a quantum computer will replace the laptop or server sitting on your desk. Instead, quantum computers are being developed to tackle certain extremely complicated problems—such as modeling molecules and materials, optimizing complex systems and addressing some problems in cryptography—that could be difficult or impractical for conventional computers.


The technology is still developing, and significant technical challenges remain. But the federal government is treating quantum computing as an important emerging technology with potential national security and economic implications. 

What Does This Mean for Government Contractors? 

For government contractors, the opportunity may not be in building a quantum computer. Instead, opportunities could develop throughout the supporting ecosystem. As federal investment grows, contractors with capabilities in areas such as cybersecurity, software development, engineering, testing, advanced manufacturing, cloud computing, data analytics, systems integration and technical consulting may find opportunities to support larger prime contractors, research organizations and federal agencies. 


For example, Defense Advanced Research Projects Agency (DARPA) continues to actively engage industry on quantum technology.  Its Quantum Benchmarking Initiative is examining approaches to developing utility-scale, fault-tolerant quantum computing, including independent verification and validation. DARPA specifically encourages participation from traditional defense contractors, corporations and startups, and maintains resources for small businesses interested in its programs. 


For contractors looking for potential business-development opportunities, this makes quantum technology worth monitoring—not necessarily because every company needs to become a quantum computing company, but because new technology programs often create requirements for a much broader network of supporting contractors and suppliers. 


DARPA is a U.S. Department of Defense agency that funds and manages high-risk, high-payoff research intended to develop technologies that could provide major advantages for national security. For government contractors, DARPA is relevant because it works directly with industry, universities, startups, and research organizations to develop emerging technologies. 

There Is Also a Cybersecurity Side to the Story 

Quantum computing presents an opportunity, but it also creates a cybersecurity issue that government contractors should understand. A sufficiently powerful quantum computer could eventually threaten some of the encryption methods currently used to protect sensitive information. This is why the federal government and cybersecurity community are already working on post-quantum cryptography (PQC)—security methods designed to withstand attacks from future quantum computers. 


National Institute of Standards and Technology (NIST) has already finalized three federal post-quantum cryptography standards and is encouraging organizations to begin transitioning to quantum-resistant technology. NIST notes that the transition can take years because organizations must identify where vulnerable cryptography is being used and update systems, products and services accordingly. 


For government contractors, this is an important distinction: you do not need to operate a quantum computer for quantum technology to affect your business. 


Contractors that maintain federal systems, develop software, manage sensitive information or provide cybersecurity services may eventually need to address quantum-resistant encryption as part of their technology and security planning. 


What Should Contractors Do Now? 

There is no need for most small and midsize contractors to make major investments in quantum computing today. A more practical approach is to begin monitoring the technology and understanding where it could intersect with your business. Consider: 


  • Monitor federal opportunities. Watch agencies such as DARPA, NIST, NSF and the Department of Defense for quantum-related solicitations, research programs and technology-transition opportunities. 


  • Look beyond the prime contract. Quantum initiatives will require suppliers, cybersecurity companies, engineers, software developers, testing organizations and other specialized service providers. 


  • Talk with your technology partners. Ask whether the systems and products you rely on have a plan for transitioning to post-quantum cryptography. 


  • Assess long-term data protection. Information that must remain confidential for many years may warrant particular attention to emerging quantum-related risks. 


  • Build awareness internally. Even if quantum computing is not part of your current contract portfolio, understanding the technology can help identify future teaming and subcontracting opportunities. 


The federal government's growing investment in quantum computing signals that the technology is moving from primarily academic research toward a broader national technology and industrial strategy. For government contractors, the takeaway is not that quantum computing is about to transform every federal program.


Rather, the supporting ecosystem is beginning to take shape—and contractors that understand where their existing capabilities fit may be better positioned to recognize opportunities as they emerge. The quantum era is still developing. But for companies serving the federal government, it is a technology worth having on the radar now. 


Resources for government contractors include: 


  • DARPA Industry Opportunities: DARPA provides information on current opportunities, including Broad Agency Announcements, Requests for Proposals and Requests for Information, as well as resources for small businesses. 


  • DARPA Quantum Benchmarking Initiative: Current quantum-related research and technology-development opportunities can be monitored through DARPA's Quantum Benchmarking Initiative. The initiative is examining whether utility-scale quantum computing can become practical and is currently soliciting participation in several areas. 


  • NIST Post-Quantum Cryptography: NIST's resources explain the new quantum-resistant cryptography standards and provide guidance for organizations planning their transition. NIST recommends that organizations begin preparing for migration to post-quantum cryptography. 


  • National Quantum Initiative: Quantum.gov provides information on federal quantum research, programs and initiatives across the government, including activities involving quantum computing, networking and sensing. 

Read more

FAQ

Frequently Asked Questions

What’s the difference between a PEO and an ASO?

Do I lose control of my employees under a PEO arrangement?

Can C2 help with government contractor compliance?

Is the HR platform included with your services?

What size businesses does C2 work with?